

Reverse Engineer, Analyze, and Fuzz Firmware for Operational Technology Environments
REAFFIRM automates Operational Technology (OT) firmware vulnerability detection and FBOM generation, further augmented by cyber digital twin and integrated harnessing tools. Designed specifically for securing Operational Technology, REAFFIRM helps organizations protect the firmware that powers critical industrial systems, embedded devices, and OT infrastructure.
The Challenge: Firmware Is a Major Operational Technology Security Gap
Firmware is one of the most significant and under-protected attack surfaces in Operational Technology environments.
83% of businesses have faced a firmware attack in the past two years [Microsoft], yet most security investments remain focused on IT networks and software rather than OT firmware.
In Operational Technology systems, where availability, reliability, and real-time control are critical, firmware often comes without source code that could be inspected for security issues, depends on specialized hardware, and lacks mature analysis tools. This makes it a prime target for attackers seeking to compromise industrial control systems, embedded networking devices, and OT assets.
The Solution: REAFFIRM for Securing Operational Technology
REAFFIRM makes firmware security faster, smarter, and easier. With support for leading architectures, 32/64 bit versions of x86, ARM, PPC, MIPS, RISC-V, and more, it takes you from raw firmware packages to meaningful results in one seamless process.
REAFFIRM enables security teams to:
- Unpack & Extract firmware updates effortlessly
- Reveal firmware functionality using deep static analysis
- Uncover hidden weaknesses through targeted fuzzing
- Work your way with the Web UI, Jupyter Notebook, CLI, or Python API
These capabilities are purpose-built to support securing Operational Technology systems, where firmware vulnerabilities can directly impact physical processes and safety.
Key Benefits for Operational Technology Seurity Teams
Faster Insights for OT Firmware Analysis
Reduce the time, expertise, and effort needed to analyze Operational Technology firmware using automated workflows.
Higher Accuracy in Securing Operational Technology
Improve detection of OT firmware security risks with consistent, repeatable analysis techniques.
Actionable Results for OT Security
Provide clear, actionable intelligence for security analysts and reverse engineers working to secure Operational Technology environments.
Seamless Integration into Existing OT Workflows
Support multiple analysis workflows in a user-friendly environment designed for real-world Operational Technology use cases.
System and Workflow
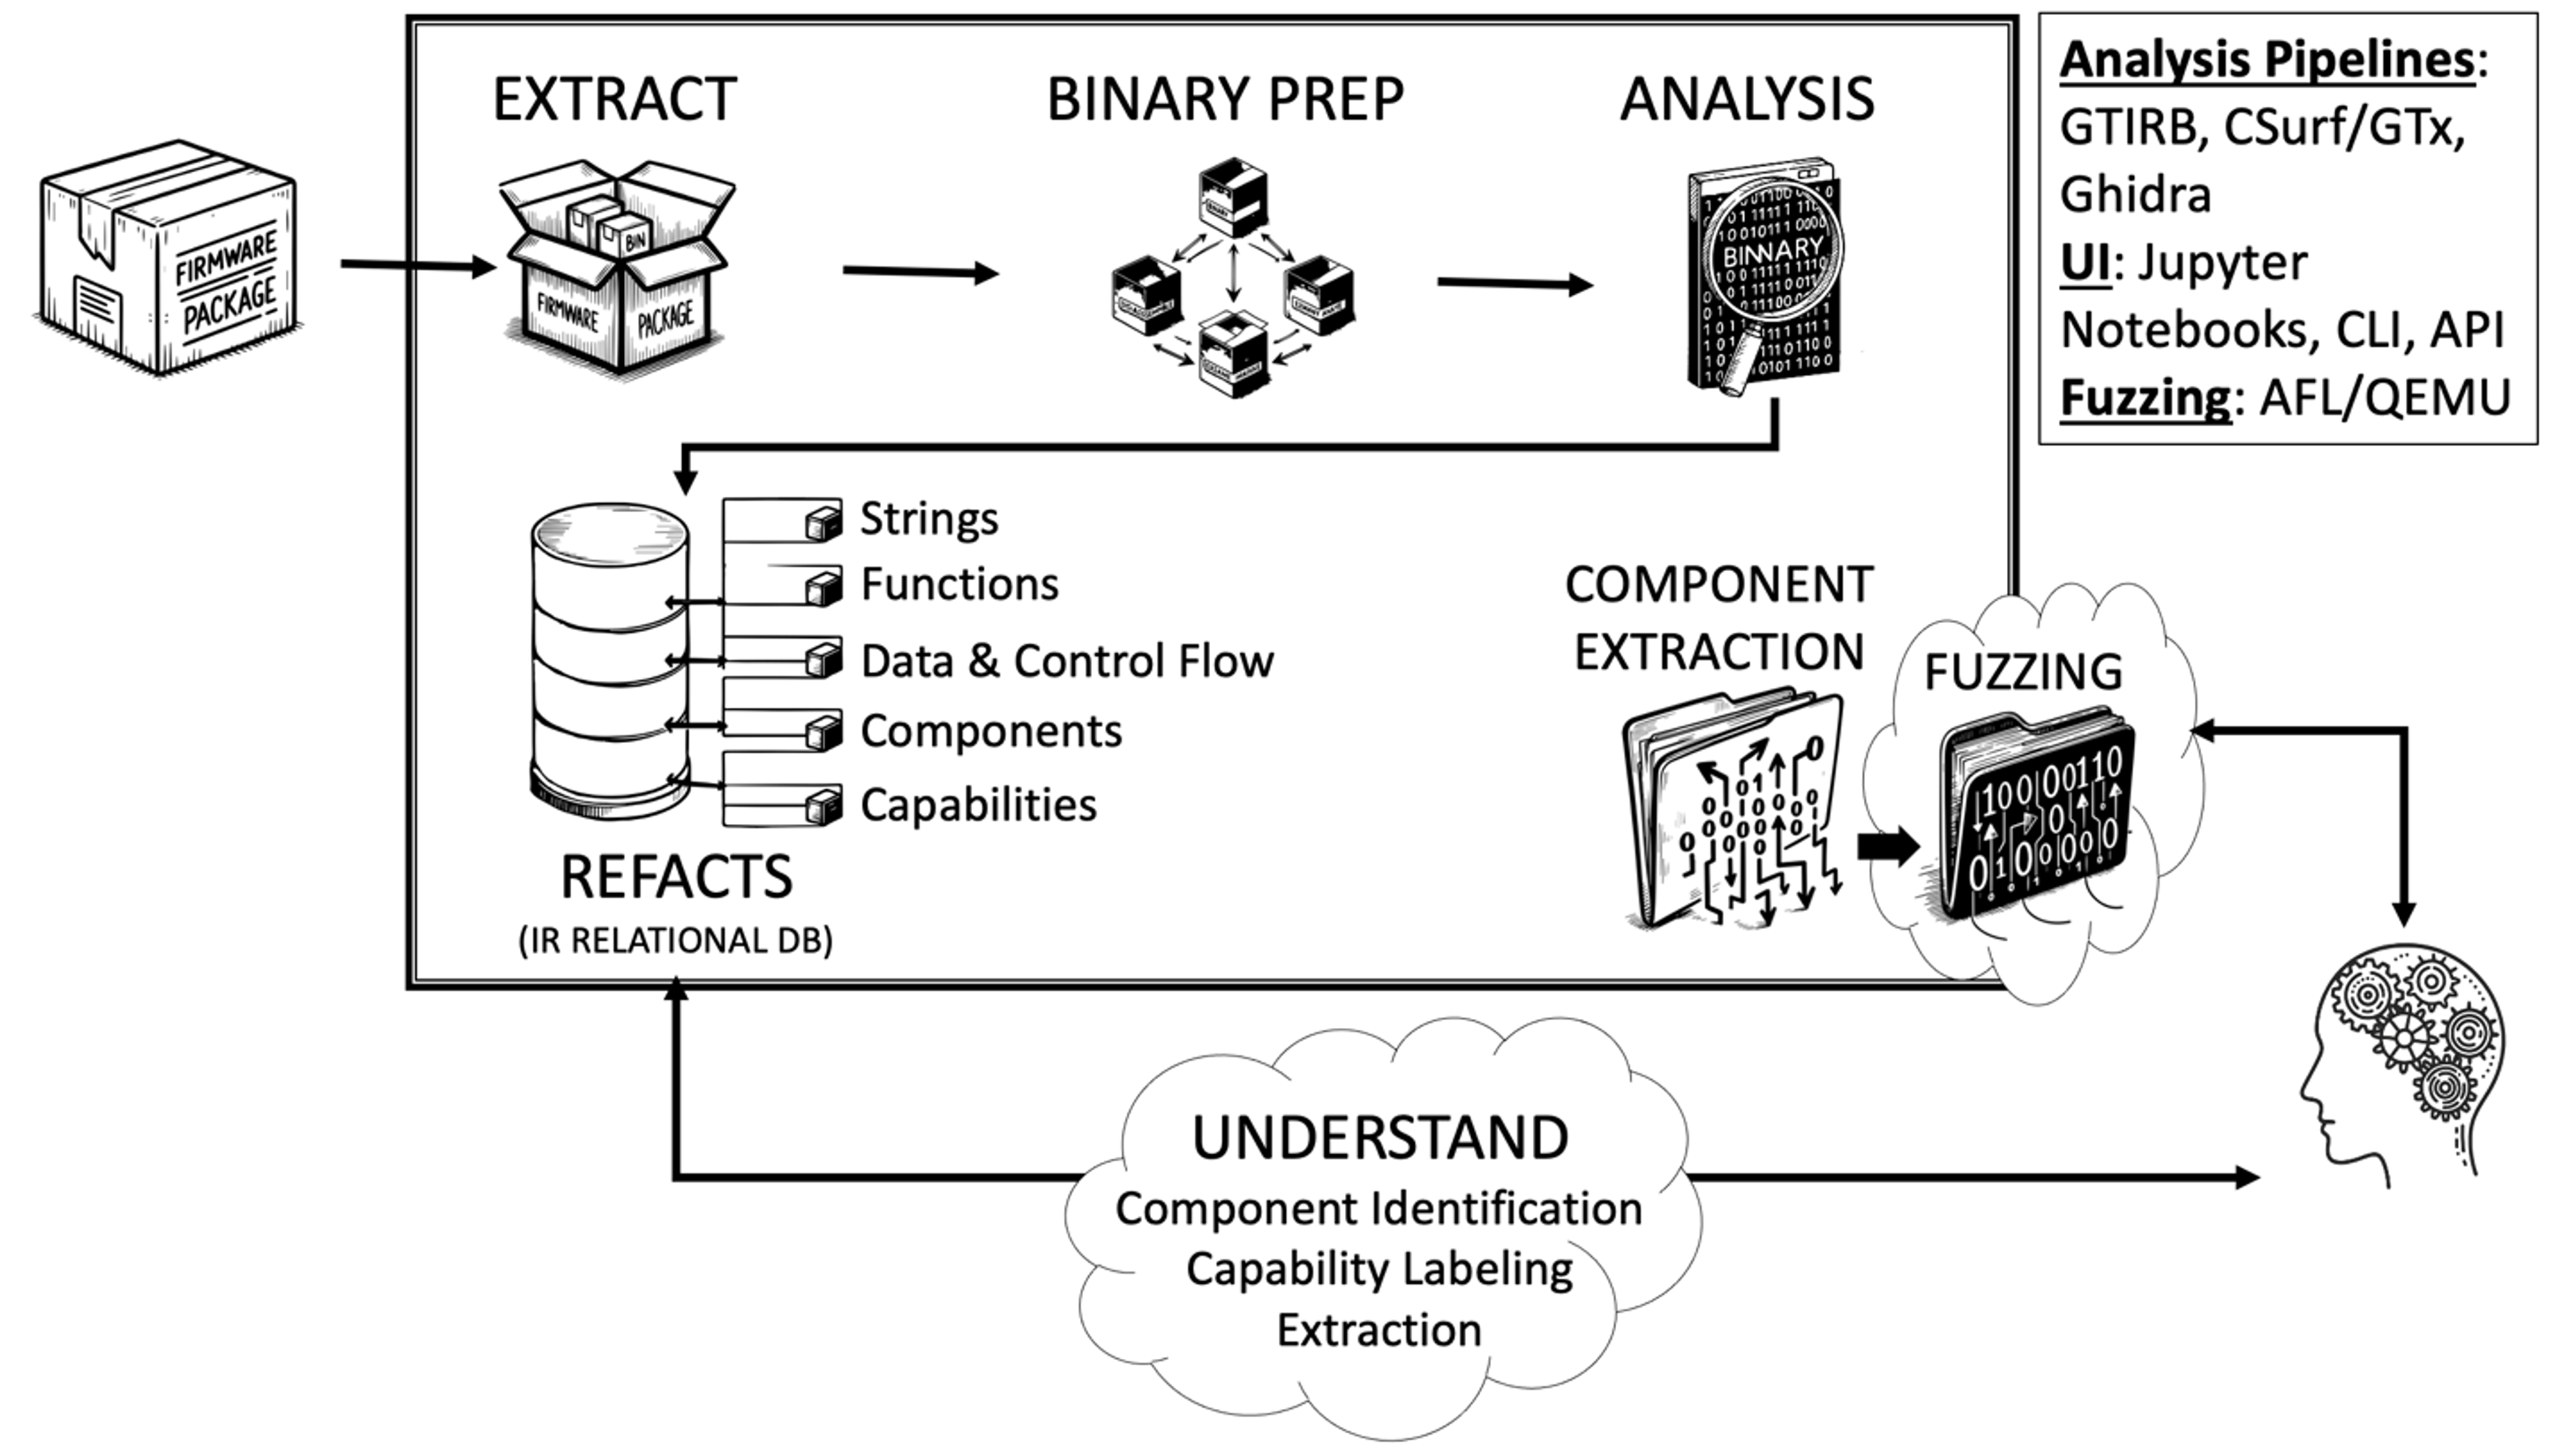
User Interaction: available to query database and interact with analysis, extraction, and fuzzing
Automation: Python API, Command Line, and Jupyter Notebooks to integrate into your workflow
Proven Performance in Operational Technology Firmware Securityovenoven
REAFFIRM has demonstrated measurable success in real-world Operational Technology scenarios:
- Validated against 1,111 firmware images spanning 32 CPU architectures, including OpenWrt builds, UEFI images and bootloaders.
- Case Study: A major defense contractor and government angecy licensed REAFFIRM to accelerate reverse engineering and strengthen firmware security.
REAFFIRM for Your Operational Technology Environment Your
- Flexible licensing and subscription models
- Available on-premises for sensitive OT environments
- Expert support from firmware analysis specialists, delivering full reverse engineering and security evaluations tailored to Operational Technology systems
Securing Operational Technology Starts at the Firmware Level Your
The result is quicker, more accurate insights with less effort. REAFFIRM streamlines complex firmware analysis, empowers OT security teams, and delivers the actionable intelligence needed to stay ahead of threats targeting Operational Technology and industrial systems.
